
Hey,
Last week was about the month-three wall. This week is about the exam many of you are working towards right now: Security+. If you're studying for it, or putting it off, this issue is for you.
🔥 THIS WEEK'S INSIGHT: Grinding Questions Isn't Studying
Here's a pattern I see constantly. Someone works through five hundred practice questions, watches the score creep up, books the exam, and fails.
The problem isn't effort. It's what they did with the wrong answers.
A red cross and a score tell you nothing. If you get a question wrong and just move on, or worse, memorise the right answer, you've learned that one question. The real exam will phrase it differently, and you'll be back where you started.
What actually works is asking one thing every time you get a question wrong: why was my answer wrong, and why was the right one right? Usually it's one of three things:
A concept gap. You didn't understand the idea. Go back and learn it properly.
A confusion between similar terms. Think IDS versus IPS, or authentication versus authorisation. Write the difference down in your own words.
A misread. You knew it, but missed "best," "first," or "NOT." That's an exam-technique problem, not a knowledge problem.
Tag each wrong answer with its type, and your weak spots show up fast.
Study by weighting, not by comfort.
SY0-701 is split into five domains, and they aren't equal:
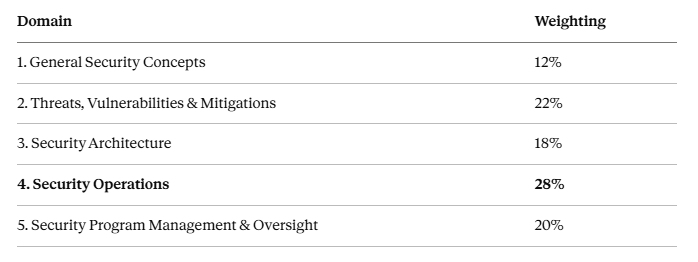
Domain 4 is the biggest slice of the exam, and it's also the most hands-on: incident response, monitoring, vulnerability management, identity and access, automation. If you're spending most of your time on the comfortable theory in Domain 1, you're studying the smallest part of the exam.
A quick word on dumps. Memorising leaked exam questions breaks CompTIA's exam rules and can cost you the certification. It also doesn't teach you anything an interviewer will test, because "why would you do that?" has no memorised answer. If a resource promises the real exam questions, walk away.
📰 ONE THING TO KNOW THIS WEEK
SY0-701 is still the current version of the exam: up to 90 questions in 90 minutes, with a passing score of 750 on a scale of 100 to 900. That's a scaled score, not a percentage, so don't aim for "just over 75%." Aim to be consistently comfortable in every domain, not only your favourites.
🛠️ FREE TOOL OF THE WEEK: The Security+ Practice Quiz
practice.mpcybersecurity.co.uk
I built this because most free practice tests do exactly what I described above: give you a score and nothing else.
200 exam-style questions, drawn 20 at a time, weighted like the real exam
Single-answer, multiple-answer, and scenario questions, not just definitions
An explanation on every question: why the right answer is right, and why the one you picked was wrong
Written by a working CISO, not scraped from a dump
Free, no signup
Use it the way I described above. Don't chase the score. Chase the explanations.
💡 CAREER ADVICE FROM THE HIRING TABLE
On exam day, manage the clock before you manage the questions.
The exam includes performance-based questions (PBQs), where you configure something or work through a scenario instead of picking an answer. They're worth the same attention as the rest, but they take far longer. A common mistake is spending twelve minutes on the first PBQ and rushing everything else.
Here's the approach that works:
Flag the PBQs and skip them. They usually appear first. Don't start there.
Answer all the multiple-choice questions first. Keep moving, and flag anything you're unsure about.
Answer every question. Leave nothing blank.
Come back to the PBQs with the time you've banked. You'll be calmer, and you'll have already warmed up.
Use any remaining time to review your flagged questions.
And a hiring-manager note: passing Security+ gets your CV past the first filter. It doesn't get you the job on its own. Once you've passed, build something you can show, because that's what answers the follow-up question, "so what have you actually done?"
🎯 YOUR ONE ACTION THIS WEEK
Take one 20-question quiz at practice.mpcybersecurity.co.uk.
Then write down the topic of every wrong answer. Not the question, the topic: "NAT," "risk matrices," "incident response phases," "certificates."
If the same topic shows up twice, that's where your next study session goes. That one list is worth more than another fifty questions.
🧰 FREE TOOLS, IF YOU HAVEN'T TRIED THEM YET
🧠 Preparing for Security+? practice.mpcybersecurity.co.uk gives you an explanation on every answer.
🧭 Not sure which path comes after Security+? path.mpcybersecurity.co.uk turns your background and working style into one recommended path.
📊 Not sure what to study next? skills.mpcybersecurity.co.uk shows exactly what's missing for your target role.
📄 Ready to apply, but hearing nothing? The CV checker shows you what the machine sees first: [add CV checker URL]
All free. No signup required to see your results.
🔜 WHEN YOU WANT SOMEONE TO TELL YOU WHERE YOU STAND
A quiz can mark you. It can't coach you, and it can't tell you whether you're actually ready to book the exam.
That's what the CTRL+ALT+DEFEND Community on Skool is for.
Timed mock exams. Full 90-question, 90-minute practice runs, so exam day isn't the first time you've felt the clock.
Weak-area tracking. See which domains are costing you points, so you study what you're actually failing.
Weekly live Q&A, direct with me. Bring whatever won't stick, and I'll explain it and give you a clear study direction.
Daily scenario questions and weekly practical challenges, so what you learn for the exam turns into the judgment an employer wants.
No guarantees. Just a place where you don't have to guess whether you're ready.
👉 Join here: https://www.skool.com/mpcyber/about
Hit reply and tell me which domain you find hardest. I read every one, and it helps me decide what to cover next.
See you next week.
Marius Poskus Global VP of Cybersecurity / CISO CTRL+ALT+DEFEND