
Issue #6 — The GitHub Portfolio Checklist (What Hiring Managers Look For in 30 Seconds)
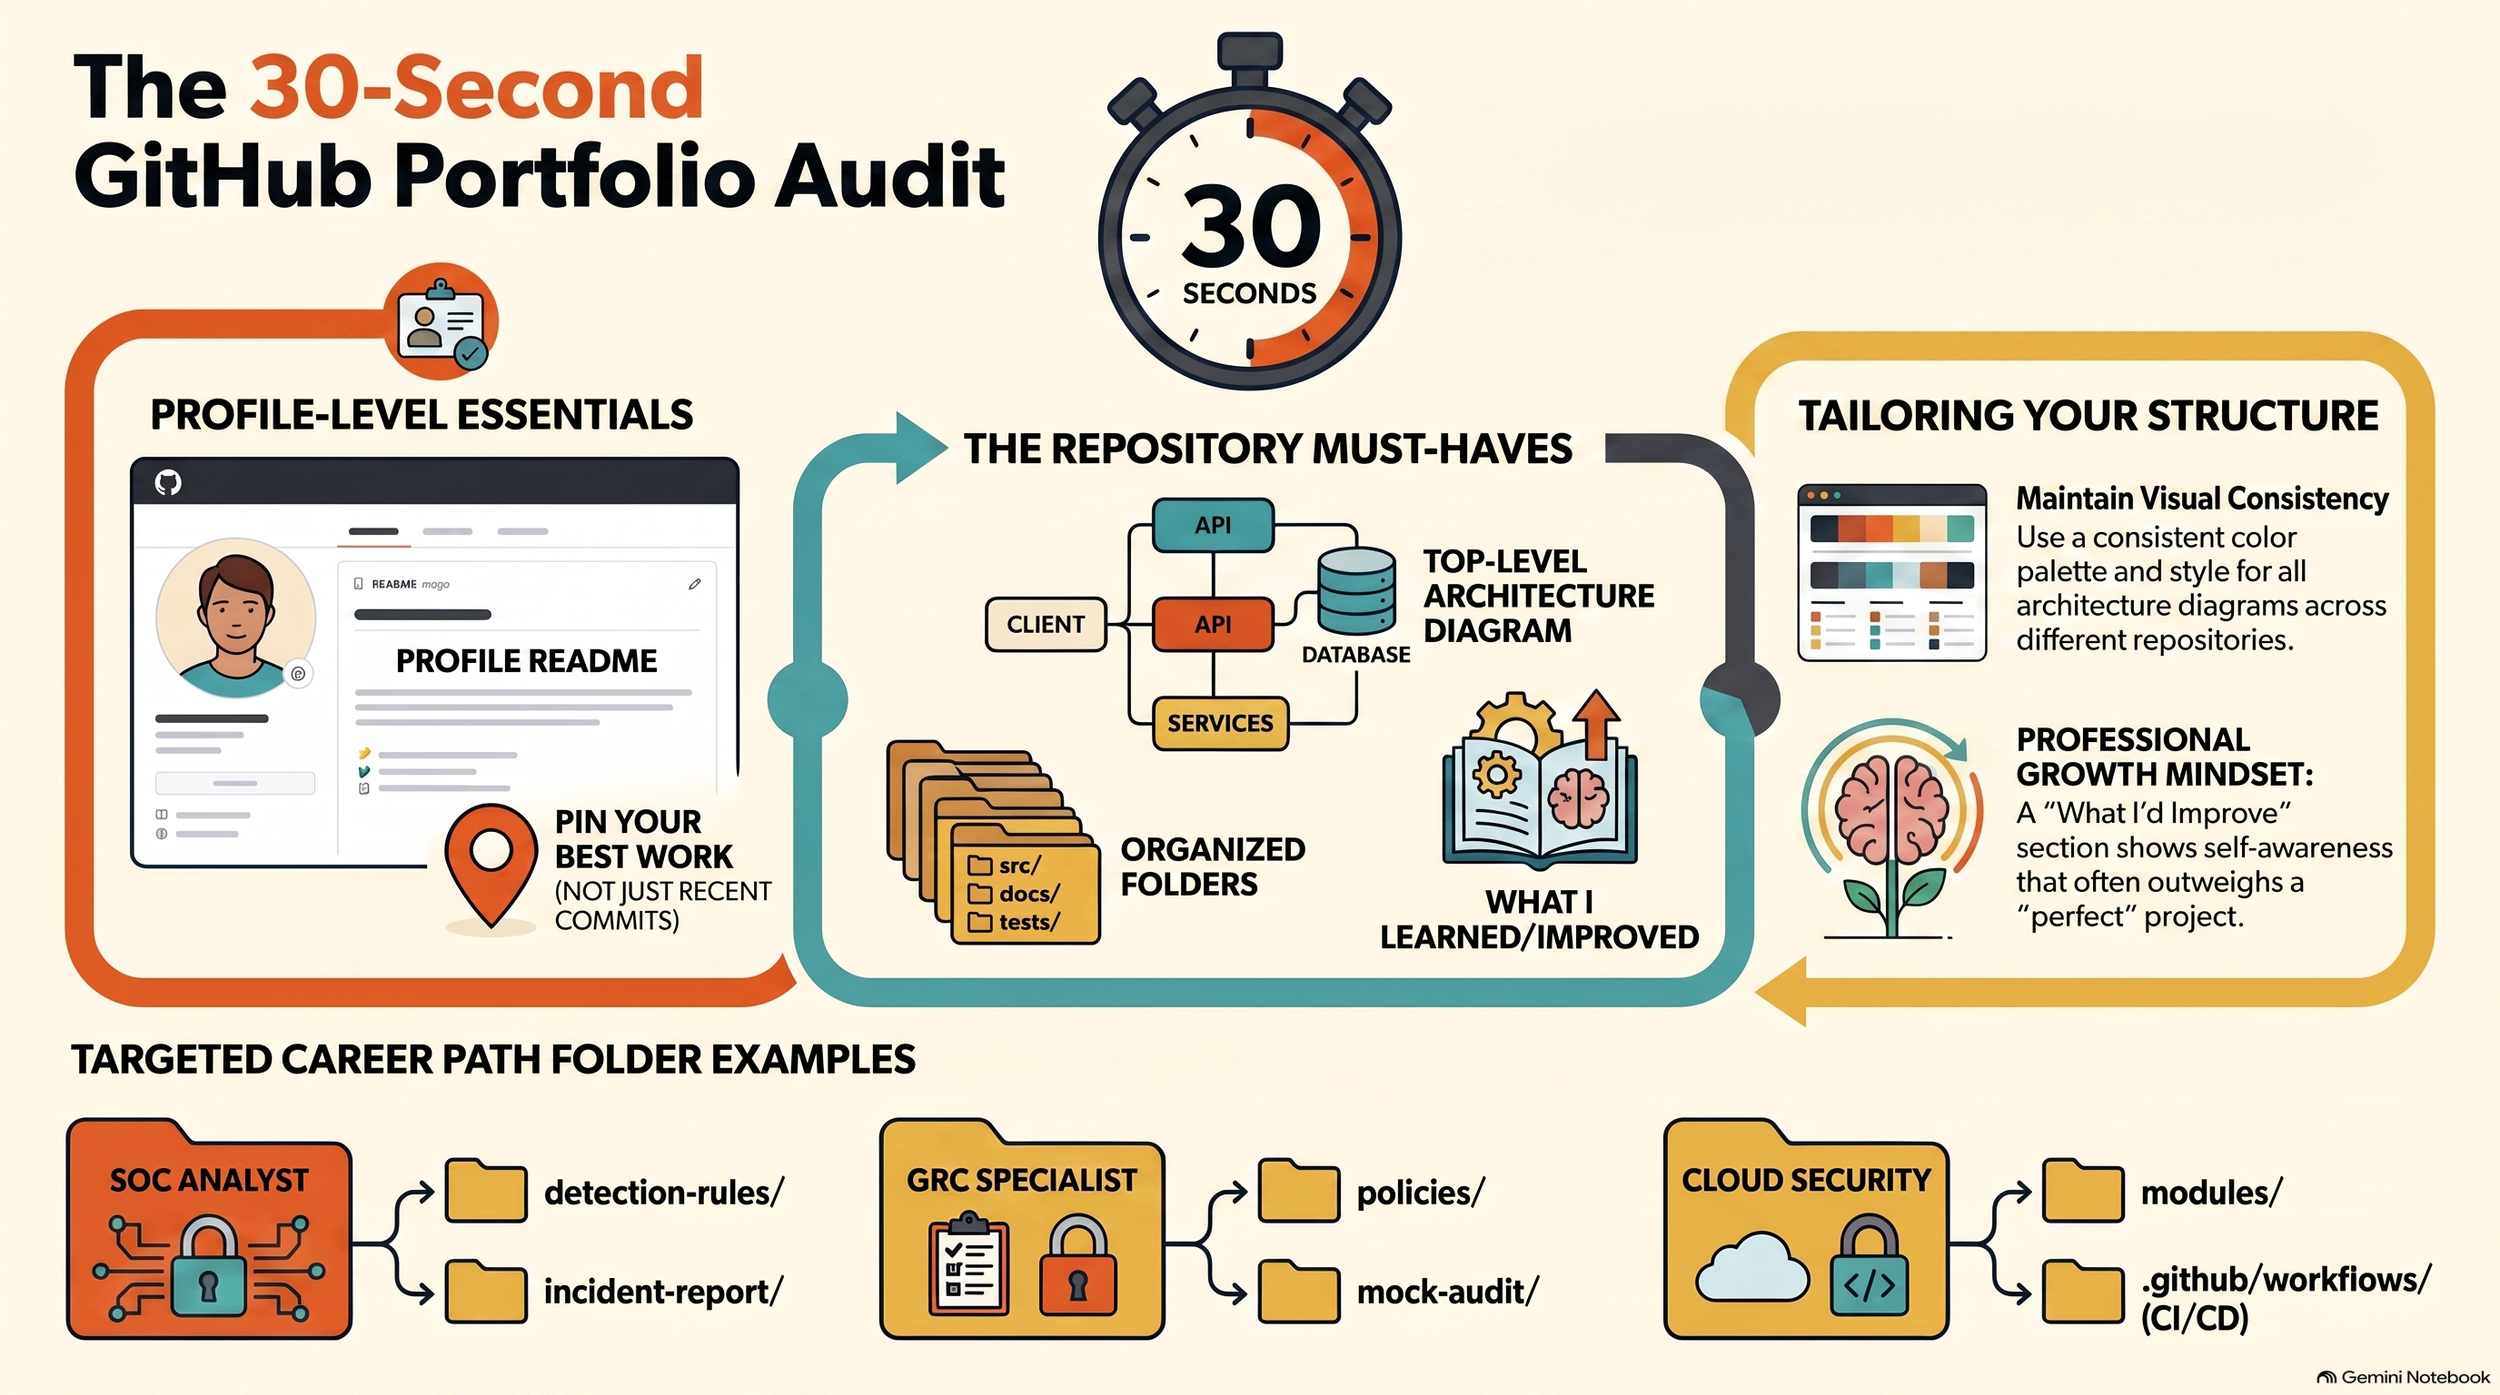
Github Portfolio Checklist
🔥 THIS WEEK'S INSIGHT: The 30-Second Test
I have 200 applications. I click maybe 60% of the GitHub links. Of those, I decide whether to look further in 30 seconds. This isn't a metaphor, it's roughly how long I actually spend before deciding your repo is worth more of my time.
Here's the exact checklist I run, whether I realise I'm running it or not.
Profile level, before I even open a repo:
Is there a profile README? (Most candidates don't have one, and it's the first thing that appears on your GitHub homepage)
Is the profile picture professional?
Are the pinned repositories your BEST work, or just your most recent commits?
Repository level, for whichever project I click into:
Does the README exist, and does it load without broken images?
Is there an architecture diagram, and is it the first thing I see, before any text?
Is the code organised into logical folders, or dumped in the root directory?
Is there a "What I Learned" section that's specific, not generic?
Is there a "What I'd Improve" section at all?
That last one matters more than people realise. I've changed my opinion of a candidate specifically because of a well-written "What I'd Improve" section. It shows self-awareness and growth mindset in a way that a perfect-looking project never can.
The fastest way to test your own portfolio: ask a friend outside cybersecurity to look at your top repo for 30 seconds, then explain back to you what it does. If they can't, your README isn't clear enough, even a non-technical reader should understand the WHAT and WHY, even if not the technical HOW.
📰 ONE THING HAPPENING IN CYBERSECURITY THIS WEEK
Two new videos went up this month that connect directly to this issue. "5 Cybersecurity Certifications You Should Avoid in 2026" makes the case that the money spent on the wrong certification is almost always better spent building the exact kind of portfolio this issue describes. And "Why I'd Choose GRC Over Pentesting in 2026" shows that even in a non-technical path like GRC, a documented risk assessment or mock audit in your portfolio carries the same weight as a technical project does for an engineering role. The 30-second test applies no matter which path you're on.
🛠️ FREE TOOL OF THE WEEK: draw.io (Revisited, With a Twist)
I covered draw.io back in Issue #3 for building your architecture diagram. Here's the addition this week: keep a consistent visual style across every diagram in your portfolio. Same colour palette, same shape conventions, same labelling approach.
Why this matters: when I click through three of your repos and see the same diagram style each time, it signals professionalism and consistency, not just one lucky project. It's a small detail that very few candidates think to do, and it's genuinely free to implement, it just takes discipline.
💡 CAREER ADVICE FROM THE HIRING TABLE
Your GitHub repository structure should match your target career path, not be generic. A SOC portfolio needs a detection-rules/ folder and an incident-report/ folder. A GRC portfolio needs policies/ and mock-audit/ folders. A cloud security portfolio needs modules/ and a .github/workflows/ folder showing your CI/CD security pipeline.
If your repo structure could belong to any career path, that's often a sign the project itself hasn't been tailored enough to the specific role you're targeting.
🎯 YOUR ONE ACTION THIS WEEK
Open your best repository right now. Check for exactly three things: a README that explains what and why, an architecture diagram near the top, and a "What I'd Improve" section. Add whichever one is missing before you close this email. That's the highest-leverage twenty minutes you'll spend on your portfolio this month.
🔜 WANT SOMEONE TO ACTUALLY LOOK AT YOURS?
Here's the honest limitation of a newsletter: I can give you the checklist, but I can't run it against YOUR specific repository and tell you what's actually missing. That requires someone looking at your actual work.
That's exactly what happens inside the CTRL+ALT+DEFEND Community. Weekly live Q&A where you can bring your GitHub and get it reviewed on the spot. Portfolio roasts, the same 30-second test I just described, applied directly to your project, with specific feedback on what to fix. Plus every digital product I've built, including the full GitHub Portfolio Blueprint with repository templates for all seven career paths, included at no extra cost.
I'll also say this plainly, because I think it matters: I'm not promising this guarantees you a job. Nobody honestly can. What I can promise is direct, ongoing access to someone who has personally clicked thousands of these links and can tell you exactly what's working and what isn't.
Join here: https://www.skool.com/cybersecurity-careers-guide-1773/about
If you just found a missing "What I'd Improve" section in your top repo, fix it before you do anything else today. Then forward this issue to someone whose GitHub you've always suspected needs the same fix.
See you next week.
Marius Poskus Global VP of Cybersecurity / CISO CTRL+ALT+DEFEND
→ YouTube: youtube.com/@mpcybersecurity
→ Skool Community: https://www.skool.com/cybersecurity-careers-guide-1773/about
→ LinkedIn: linkedin.com/in/marius-poskus
→ Website: mpcybersecurity.co.uk
→ TikTok: @mariusposkus0